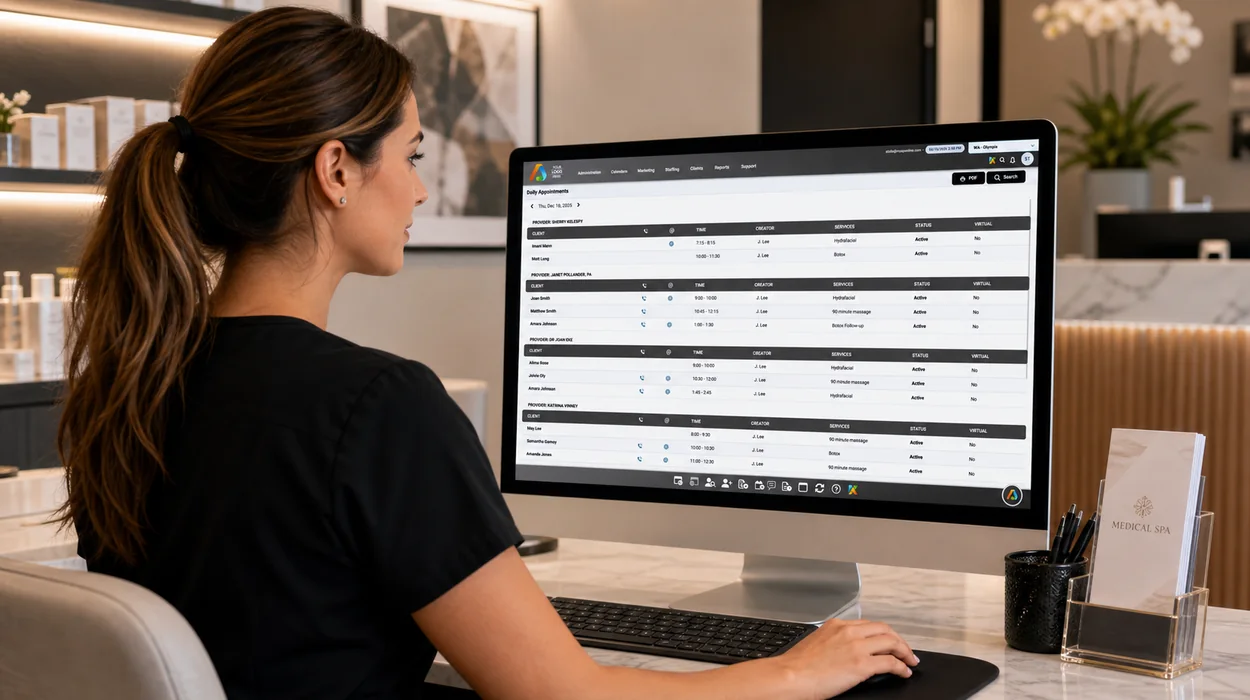

Choosing medical spa software involves more than comparing scheduling, payments, and treatment documentation features. Medical spas handle sensitive patient information, including health histories, treatment records, consent forms, and before-and-after photographs.
Protecting that information is an important part of selecting a software vendor. A platform advertised as HIPAA-compliant med spa software is not automatically the right choice for your practice.
Owners and managers should evaluate how the vendor stores patient information, controls access, handles security incidents, and meets its contractual responsibilities. This medical spa software security checklist can help you compare platforms before signing an agreement.
This article provides general information about medical spa software and HIPAA vendor due diligence. HIPAA applicability depends on a practice's legal status and activities. State privacy laws may impose additional requirements. Consult qualified legal, privacy, or security professionals when evaluating your obligations.
Medical spas operate at the intersection of healthcare and aesthetics. Although many aesthetic treatments are elective and paid for out of pocket, medical spas may still collect sensitive health information.
Whether HIPAA applies depends on the practice's legal status and activities, not simply whether treatments are cosmetic or covered by insurance. A medical spa may qualify as a HIPAA-covered entity if it meets the applicable definition of a healthcare provider and conducts certain standard electronic healthcare transactions.
Even when a practice is not a HIPAA-covered entity, other federal or state privacy laws may govern how it collects, stores, and shares patient information. Before choosing software, determine which privacy and security requirements apply to your business.
Medical spa software may store:
When information qualifies as protected health information (PHI), applicable HIPAA requirements govern how covered entities and their business associates may use and disclose it. Your software vendor's handling of this information should be central to your evaluation.
Before-and-after photography is common in medical aesthetics, but patient photographs can create privacy risks when they contain a face, tattoos, scars, or other recognizable details. When connected to an identifiable patient's healthcare information and maintained by a covered entity or business associate, a photograph may constitute PHI.
Before selecting software, confirm that patient photographs are stored securely, access can be restricted by employee role, images are connected to the correct patient record, access and changes are captured in audit logs, and photographs can be included in patient record exports.
Also determine how the platform separates clinical photographs from images used for marketing. A patient's consent to treatment does not automatically authorize the use of their images in marketing.
Determine whether the vendor creates, receives, maintains, or transmits PHI on your behalf. Identify which software modules handle PHI, whether third-party integrations or subcontractors access it, and what business associate responsibilities the vendor accepts.
Questions to ask: Does the platform process or store PHI? Which services are included in its HIPAA-related contractual commitments? Do subcontractors handle patient information?
A Business Associate Agreement (BAA) establishes permitted uses and disclosures of PHI and outlines responsibilities for protecting that information.
A signed BAA does not prove that software is secure. It is one part of HIPAA vendor due diligence.
Front desk staff, providers, managers, and administrators may need different levels of access. Confirm that employees have individual accounts, permissions can be assigned by role, access can be limited by job responsibilities, multifactor authentication is supported, and employee access can be removed promptly.
Questions to ask: Can front desk employees be restricted from certain clinical records? Does the system support multifactor authentication? Can an employee account be disabled immediately?
When comparing vendors, ask how ePHI is protected during transmission and storage. Verify where information is hosted, how backups are secured, how customer data is separated, and whether photographs, attachments, exports, and integrations have any security limitations.
Do not rely on a claim such as "256-bit encryption" without understanding where and how encryption is implemented. Encryption is an addressable implementation specification under the HIPAA Security Rule in effect as of this article's preparation, which requires appropriate assessment and documentation.
Ask what the platform records and how administrators can review that activity. Confirm that relevant activity involving ePHI is recorded, logs identify individual users, changes can be traced, retention periods are documented, and logs can be retrieved during a privacy investigation.
An HIPAA compliant medical spa software platform should provide enough visibility to investigate who accessed or changed a patient record. Basic appointment history or recent login information may not provide the same visibility as comprehensive audit controls.
Confirm that treatment records are linked to the correct patient, providers can be identified in clinical documentation, digital intake and consent forms are stored appropriately, records can be corrected or amended appropriately, and authorized patient record requests are supported.
Ask whether records can be exported in usable formats and whether clinical documentation is protected from unauthorized changes. A connected EMR can make information easier to locate, but the vendor must also support appropriate security and record-access procedures.
The 21st Century Cures Act and related information-blocking regulations may affect certain healthcare providers, health IT developers, and health information networks or exchanges. These requirements do not apply identically to every medical spa or software vendor.
When evaluating an EMR, ask whether the vendor supports the record access and exchange capabilities relevant to your practice's legal obligations. Do not assume that purchasing an EMR automatically satisfies information-blocking requirements.
Ask how frequently patient data is backed up, how backups are protected, how recovery processes are tested, how customers are notified about outages, and how records can be restored during a disruption. Review recovery time and recovery point commitments, and request written information instead of relying only on verbal assurances.
Confirm that the vendor maintains an incident response process, review contractual reporting obligations, ask how quickly your practice will be notified, and determine what information the vendor provides during investigations.
HIPAA business associates generally must notify covered entities of breaches of unsecured PHI without unreasonable delay and no later than 60 calendar days after discovery. Contracts may require faster notification, and other reporting obligations may apply.
Identify which third-party services receive or access PHI, ask how subcontractor security is evaluated, confirm that required downstream BAAs are in place, and determine whether PHI is shared with analytics or advertising tools.
Before-and-after images can be valuable marketing assets, but their use must be evaluated separately from clinical documentation. Ask whether the software supports your process for recording authorizations and controlling how images are shared.
Before signing a contract, confirm your rights to access and export patient information, which data types can be exported, whether treatment notes, consent forms, photos, and attachments are included, and how long records remain accessible after cancellation.
Ask about export fees, turnaround times, available formats, and how retained copies and backups are handled. Verify these capabilities before relying on the platform for clinical recordkeeping.
Request information about the vendor's security program, independent security assessments, SOC 2 reports or other relevant audit documentation, vulnerability management, security testing, employee security training, and software update practices.
There is no official federal HIPAA certification that automatically establishes a software product's compliance. Independent assessments can provide useful evidence, but they do not guarantee HIPAA compliance.
Use this worksheet during demonstrations and contract reviews. For each vendor, record whether an item is verified, partially verified, not verified, or not applicable.
| Due Diligence Area | What to Verify | Status |
|---|---|---|
| Business associate status | Vendor's role in handling PHI is documented | [ ] |
| Business Associate Agreement | Appropriate BAA is available and reviewed | [ ] |
| Patient photography | Secure storage, access controls, and appropriate sharing options | [ ] |
| User permissions | Individual accounts and role-based access | [ ] |
| Authentication | Account protections and multifactor authentication | [ ] |
| Encryption | Appropriate safeguards for stored and transmitted ePHI | [ ] |
| Audit controls | Relevant system activity can be recorded and reviewed | [ ] |
| EMR access | Records can be retrieved and exported appropriately | [ ] |
| Backup and recovery | Documented backup and restoration procedures | [ ] |
| Incident response | Clear reporting and notification responsibilities | [ ] |
| Integrations | Third-party PHI access and safeguards are addressed | [ ] |
| Data portability | Export and termination procedures are documented | [ ] |
| Security evidence | Relevant assessments and policies have been reviewed | [ ] |
Protecting patient information starts with understanding how your software vendor handles it. Before selecting a platform, verify its contractual responsibilities, security safeguards, audit capabilities, patient photography controls, and data export procedures.
AestheticsPro offers medical spa management software with E-Records, digital forms, scheduling, client management, payments, and reporting tools designed for aesthetic practices.
Book an AestheticsPro demo to explore the platform and discuss your practice's documentation, security, and HIPAA vendor due diligence needs.
If your practice is a HIPAA-covered entity and the software handles PHI on its behalf, applicable HIPAA requirements must be addressed. The vendor may also qualify as a business associate and require a BAA.
It can. Identifiable patient photographs maintained by a HIPAA-covered entity or business associate may qualify as PHI. Their storage, disclosure, and use in marketing must be evaluated under applicable privacy requirements.
No. A BAA establishes contractual obligations but does not independently verify the vendor's security controls or guarantee compliance.
No. The U.S. Department of Health and Human Services does not provide an official certification that makes a software product automatically HIPAA compliant.
Ask about the BAA, user permissions, encryption, audit logs, patient photography, backups, breach reporting, third-party integrations, and record exports. Request written evidence for important claims.
No. Software may help organize photographs and authorization records, but your practice remains responsible for determining whether patient information can legally be used or disclosed for marketing.
No. Software is only one part of a practice's compliance responsibilities. Staff training, privacy policies, risk assessments, access management, and appropriate handling of patient information remain essential.
Related articles on growth, operations, and the systems shaping modern medical aesthetics practices.
Learn how medspa software supports secure documentation, digital consent, and HIPAA compliance to meet medical spa requirements...

Discover holiday upselling strategies to increase revenue in a med spa with packages, med spa loyalty programs, and med spa software...
Explore post-GLP-1 aesthetic treatments for volume loss, skin laxity, body contouring, and how medical spa software supports ongoing care...
Plan for the med spa holiday rush with a practical checklist for staffing, revenue, inventory, communication, and medical aesthetics software...
Learn how to plan winter aesthetic procedures before holiday events, including timing, downtime, skin quality, and natural-looking results...
See when growing med spas need med spa management software, what small business tools may outgrow, and what to look for next...
See what medical spa booking software should do before the visit, from intake and reminders to connected practice workflows...
See how spa management software can support repeat visits, memberships, stronger client retention, and long-term medspa growth...
See how AI-powered med spa software is helping aesthetic practices streamline workflows, save time, and improve the client experience...

 Login
